1.8.2: Enforce is available. Isolate is coming in a later release: its sealed workspace isn't ready yet.
Detection and monitoring are how the category watches for trouble, the smoke alarm, and it earns its place. Crawdad adds the control that acts on the alert: at Observe it freezes an agent that goes out of bounds and stops secrets (credentials and clear attempts to send data out) from leaving; Enforce adds an operating-system egress lock on macOS when agents run as a separate user; and Isolate, in a later release, adds sealed-VM containment. For an MSSP, that is the difference between reselling an alert and operating a control that contains the incident. Multi-tenant, content on-device, one console for every client.
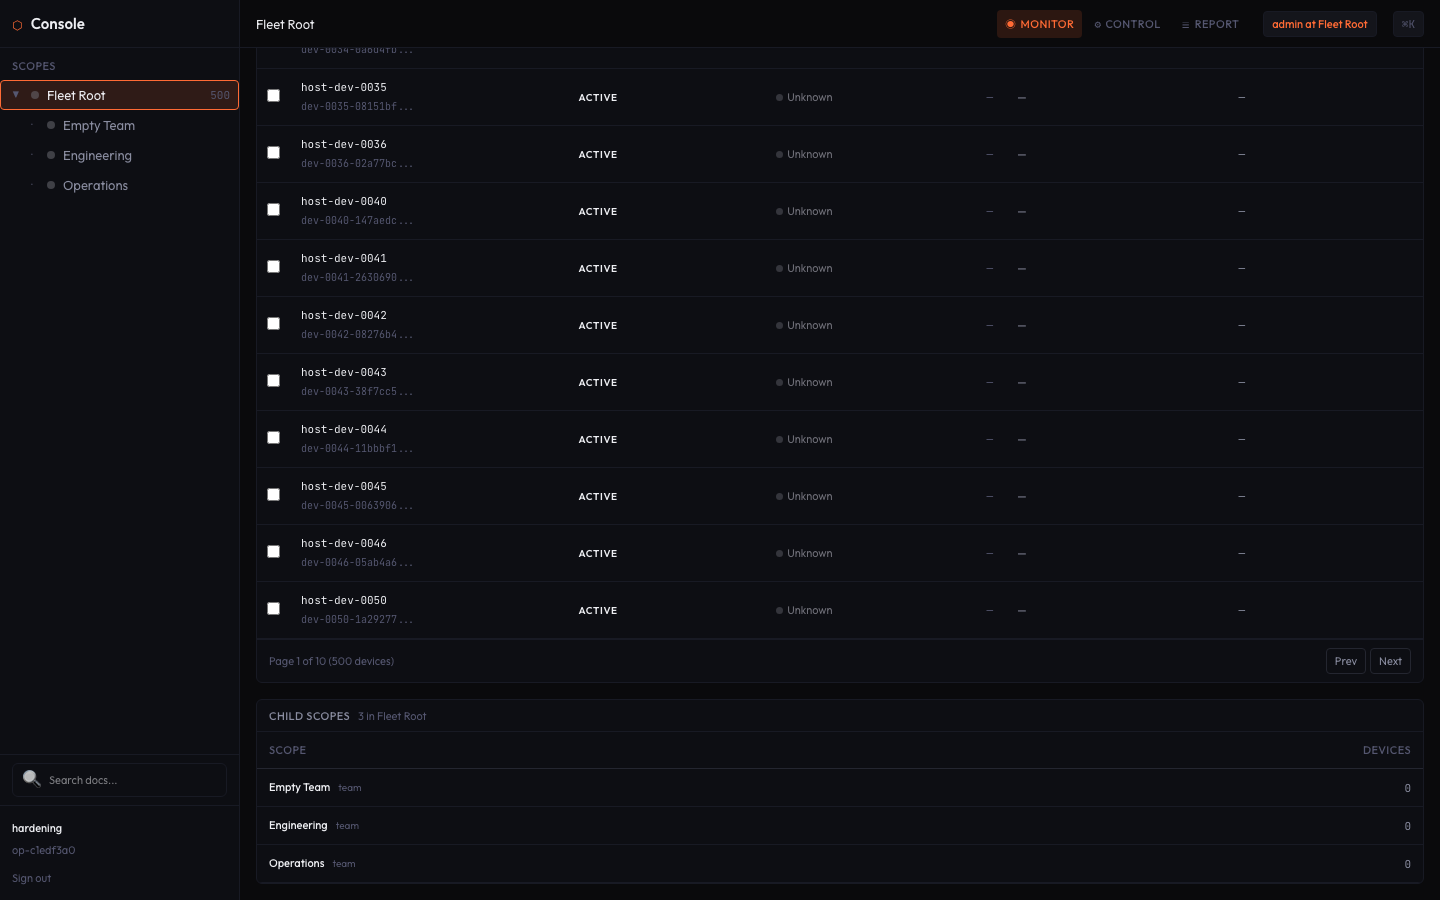
Fleet Console, per-client tenancy and enforcement posture across every client
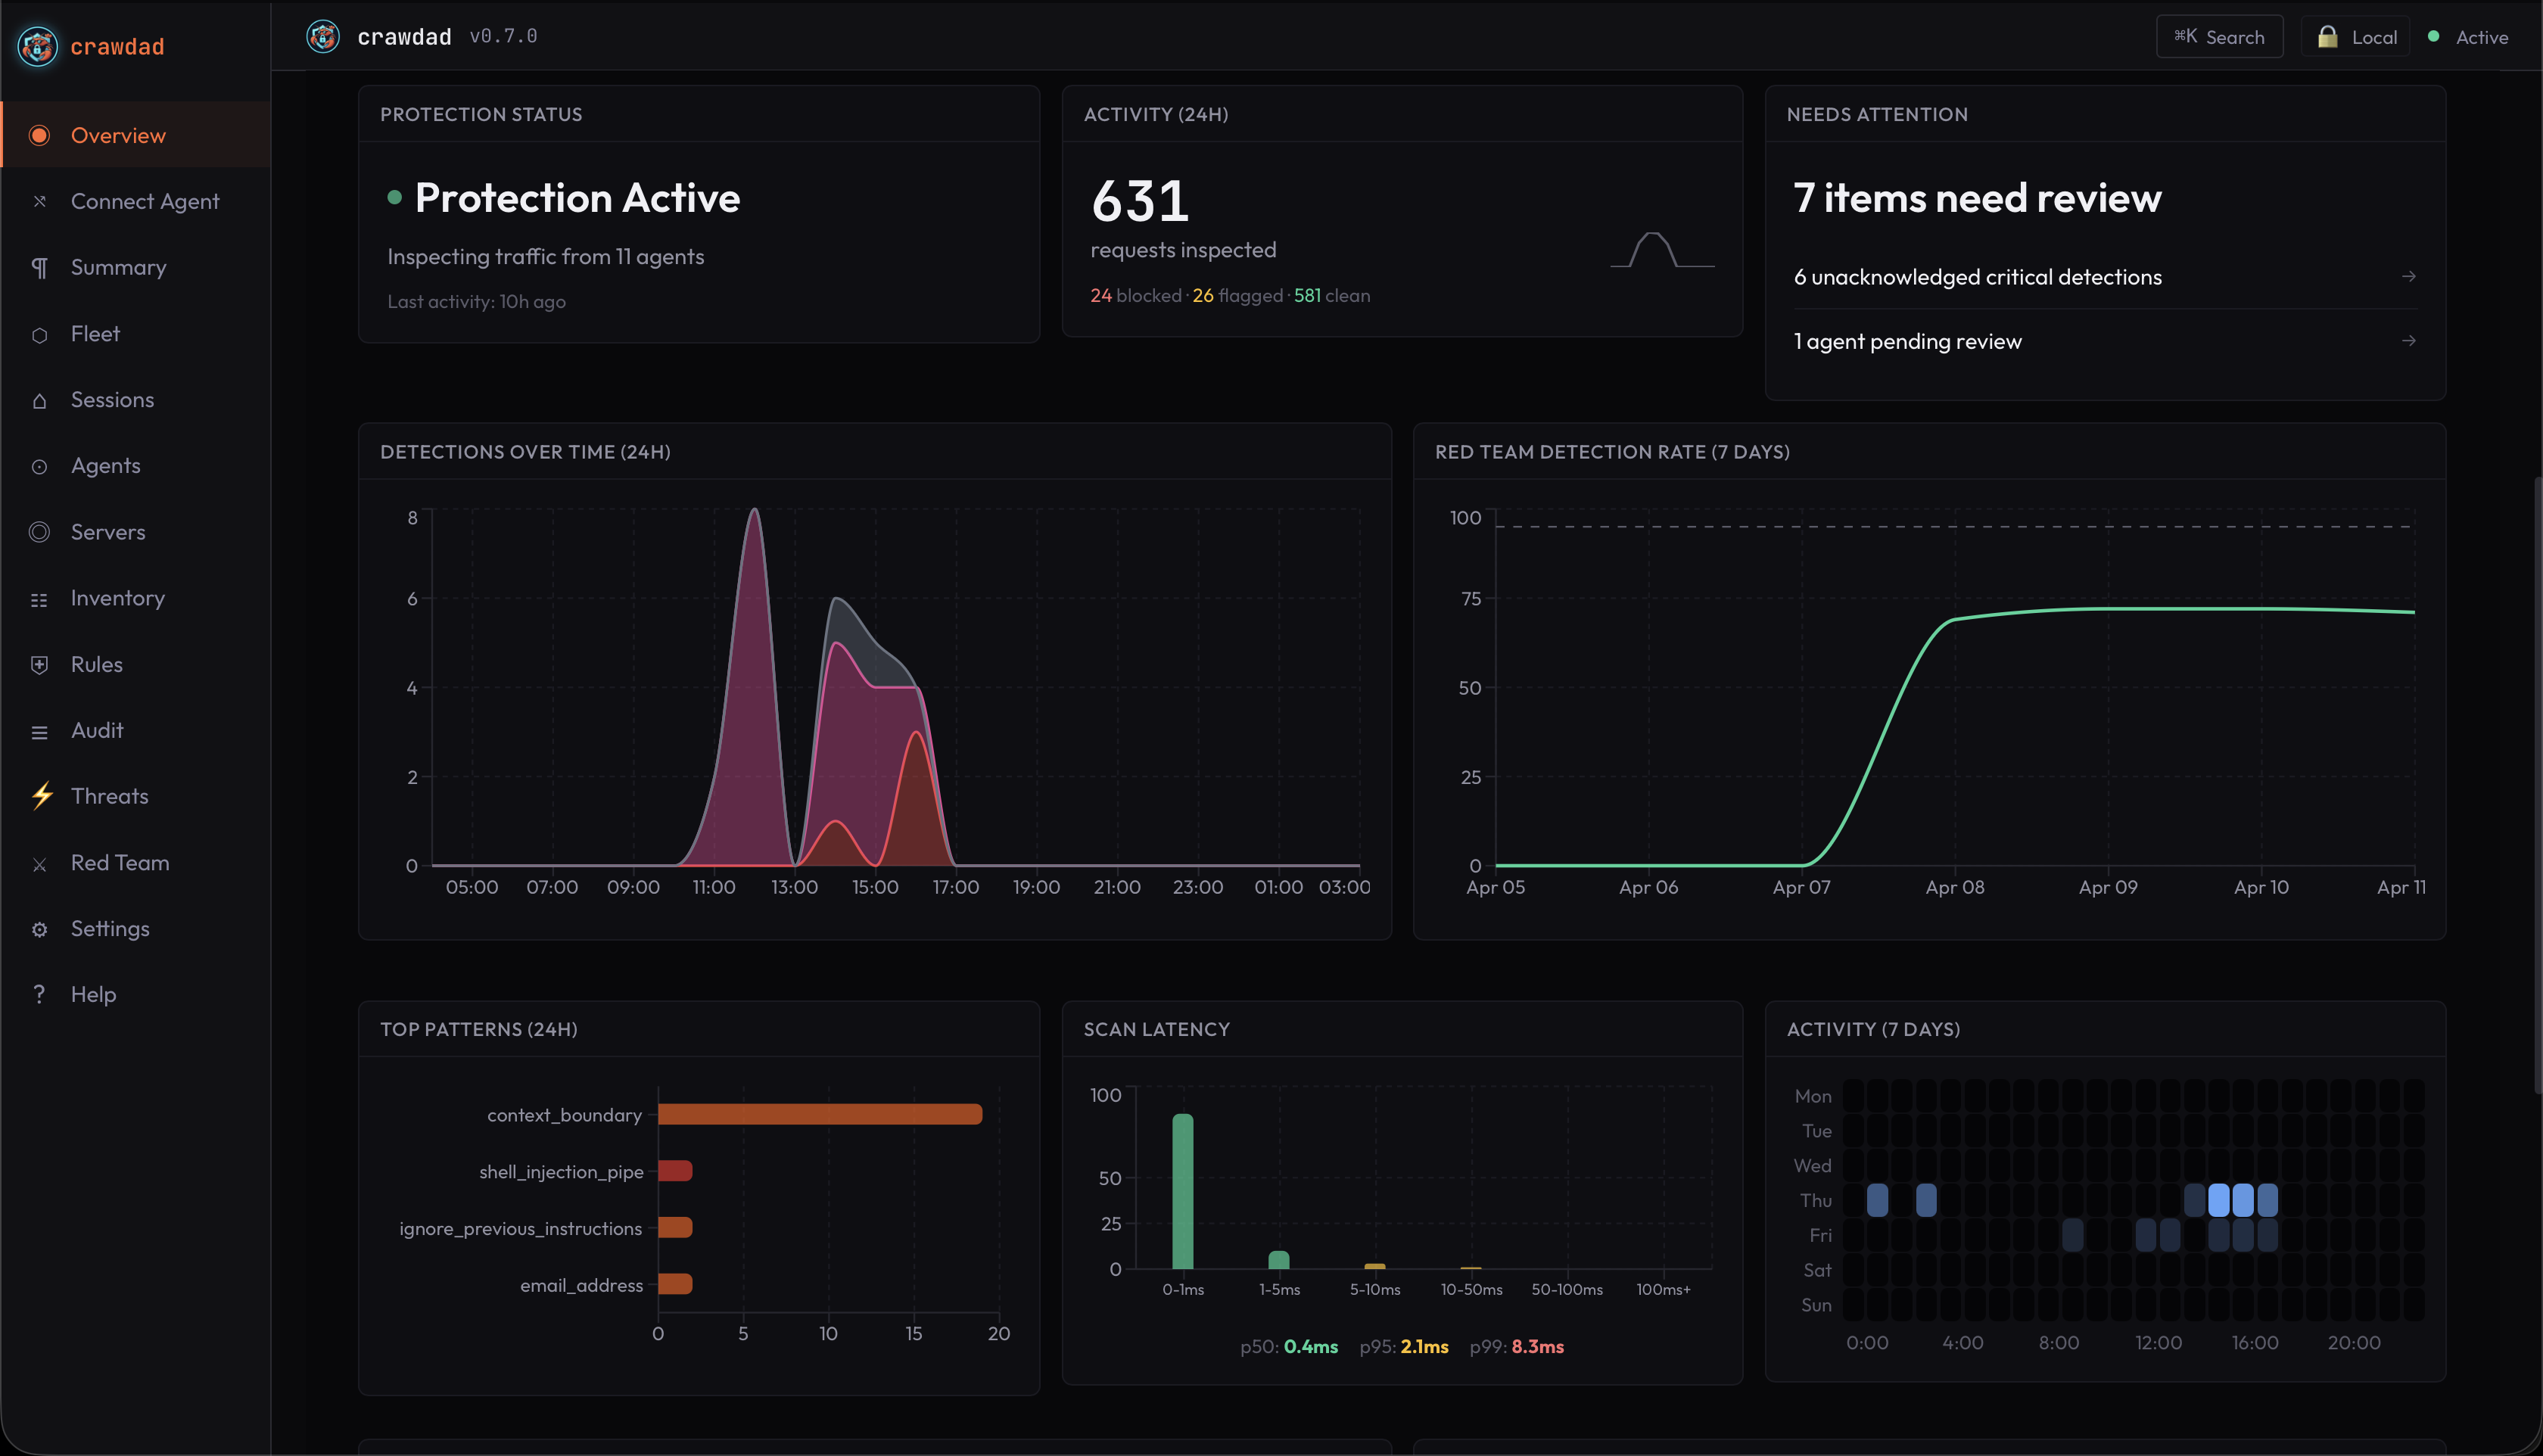
Nearly everything in the AI-security aisle today watches: it inspects traffic and raises an alert. That is real value and Crawdad does it well. But an alert is not a control. When a client asks what actually happens to a compromised agent, an MSSP wants an answer that ends in contained, not flagged.
Watching for smoke
Putting out the fire
Detection is the foundation, and Crawdad's is benchmarked in the open. Containment is the control you can point to in an incident review. Selling both, from one platform, is the differentiated MSSP offer. See detection and blocking, attack by attack →
Observe is the default; a stock device is byte-for-byte unchanged. Enforce, which leaves no path off the machine except through Crawdad on macOS when agents run as a separate user, is opt-in. Crawdad 1.8.2 has no OS network lock on Linux. The macOS pf lock loads its signed anchor and validates its rules, not yet proven at the packet level on hardware. On Linux, and when agents run as the person, Enforce works through Crawdad's own checks (the proxy, hooks and the secrets floor), and no network lock applies.
On macOS, when agents run as a separate user, Enforce installs a persistent OS default-deny egress lock (pf on macOS). A governed agent reaches only the Crawdad proxy path; everything else, including UDP/QUIC, is denied by construction.
The Isolate tier, coming in a later release, runs the agent inside a sealed workspace (a VM on Apple silicon, using Apple's Virtualization framework) whose only network interface routes through Crawdad. Escape is refused at the packet level, not by a deny rule.
Where the lock is in place, it survives a kill, so there is a deliberate recovery path, and it is deliberately hard to reach, exactly the audit story a SOC wants. When agents run as the person, a program that person runs can still change or stop Crawdad.
Platform, stated plainly. Every device runs Observe by default, so a stock device is byte-for-byte unchanged; Enforce is opt-in, and its network lock applies only on macOS, when agents run as a separate user. Crawdad 1.8.2 has no OS network lock on Linux. Read the Enforce mode guide →
An MSSP lives or dies on isolation. In Crawdad, each client is its own scope subtree with role-based access, so an analyst sees only the clients they are granted. And because the architecture is local-first and on-device, the isolation is structural, not a filter: one client's prompts and responses never leave that client's machines, so they cannot mix in a shared store because there is no shared store of content.
We prove this the honest way: a repeatable, clearly-labelled synthetic environment stands up several fictional customer orgs across real verticals and shows the isolation, posture spread, and rollup end to end. It is watermarked synthetic throughout, never presented as real customers.
The multi-tenant model, the enforcement rollout, the review queue, and the exports are part of the product, not services you assemble. Crawdad rides alongside the tools your analysts already live in.
Create an isolated client scope, then roll out with one minted enrollment key and a ready-to-run package: the enroll command, the unattended installer invocations, and the CA fingerprint pin. Devices self-enroll with no per-device signing. Push it through the RMM or MDM you already run.
Set protection per client and pin it fleet-wide (Observe or Enforce). A charter bounds what a client's agents are for, judged on the action taken, not the intent claimed; at Enforce, held actions surface in a cross-client review queue your analysts resolve from the console, releasing a session or keeping it gated.
Every device event lands in a tamper-evident, hash-chained audit log, Ed25519-signed and offline-verifiable with a standalone tool, no network and no secrets from the machine. Verifiable forensics is the report you hand a client after an incident.
Export detection and governance events to your SIEM over Splunk HEC or OpenTelemetry, so agent-layer signal lands where your analysts already work. Bill per governed device at your own price. Usage is metered through Stripe usage records, counted from the real device inventory.
Trajectory reasoning watches the shape of a whole session and holds a staged compromise for review, the exfiltration whose every single step looked fine. No runtime check catches every composed harm; this catches the staging shape, at a very low false-positive cost in our testing on benign multi-step work. The whole model runs on your own self-hosted console, with each client's content staying on their machines.
The detection engine is measured on this public corpus, the local sidecar's full multi-layer ML pipeline running in-line on proxied traffic. Detection and blocking are separate: at Observe (the default) Crawdad records detections and blocks secrets (credentials and clear attempts to send data out) in chats that go through it, in agent tool calls, and on supported AI sites, and broader blocking comes with Enforce, which is opt-in. The corpus is open so you can run it yourself. Detection and blocking, explained →
Multi-layer detection pipeline. Built in Rust. Over 5,100 automated tests across the workspace. Raw content stays on the client's machine by default, metadata-only telemetry by default (none at all when run fully offline).
AndrewSispoidis/contemporary-agent-attacks →
CC BY 4.0 · 533 attacks · 1,187 benign negatives · 15 categories
Containment is a higher-value service than a feed of alerts. Crawdad gives you something to charge for that your clients can feel.
Most of the market resells detection. An MSSP that can say "here is the agent we froze, and the record that proves it" has a story the alert-only competitor can't match, backed by proof, not adjectives. Enforce adds OS-level containment on macOS when agents run as a separate user.
Crawdad covers the agent layer that EDR, DLP, identity, and network tools don't see, and streams its signal into the SIEM your analysts already run. Additive to your SOC, not a rip-and-replace.
Agent security is nascent, and containment is the part many vendors haven't reached. The MSSPs who bring a real control now can lead their clients on it.
For your evaluation, stated plainly: by default Crawdad runs in Observe, and Enforce on macOS and Linux is opt-in. SOC 2 is architected-for, not certified, and no third-party security audit has been completed. A macOS System Extension for system-wide interception is built and pending an Apple entitlement; until it is granted, protection covers agents routed through Crawdad rather than every process on the machine. We have no customer or production-deployment claims to make in either direction. See the full trust posture →
Talk to us about becoming a Crawdad partner. We'll walk you through the containment model, the multi-tenant console, and how to position active containment against a market that mostly monitors.