Your agents already act on regulated data. Govern what they do, without moving any of it.

Crawdad governs each agent by its authorized purpose and judges the action it takes, not the intent it claims, on the machine where the agent runs. Raw content never leaves the device, so there is nothing for a vendor to hold or a breach to reach, and every decision lands in a hash-chained audit an outside party can verify without trusting us. Runs fully offline.

Talk to Us → Architecture Overview
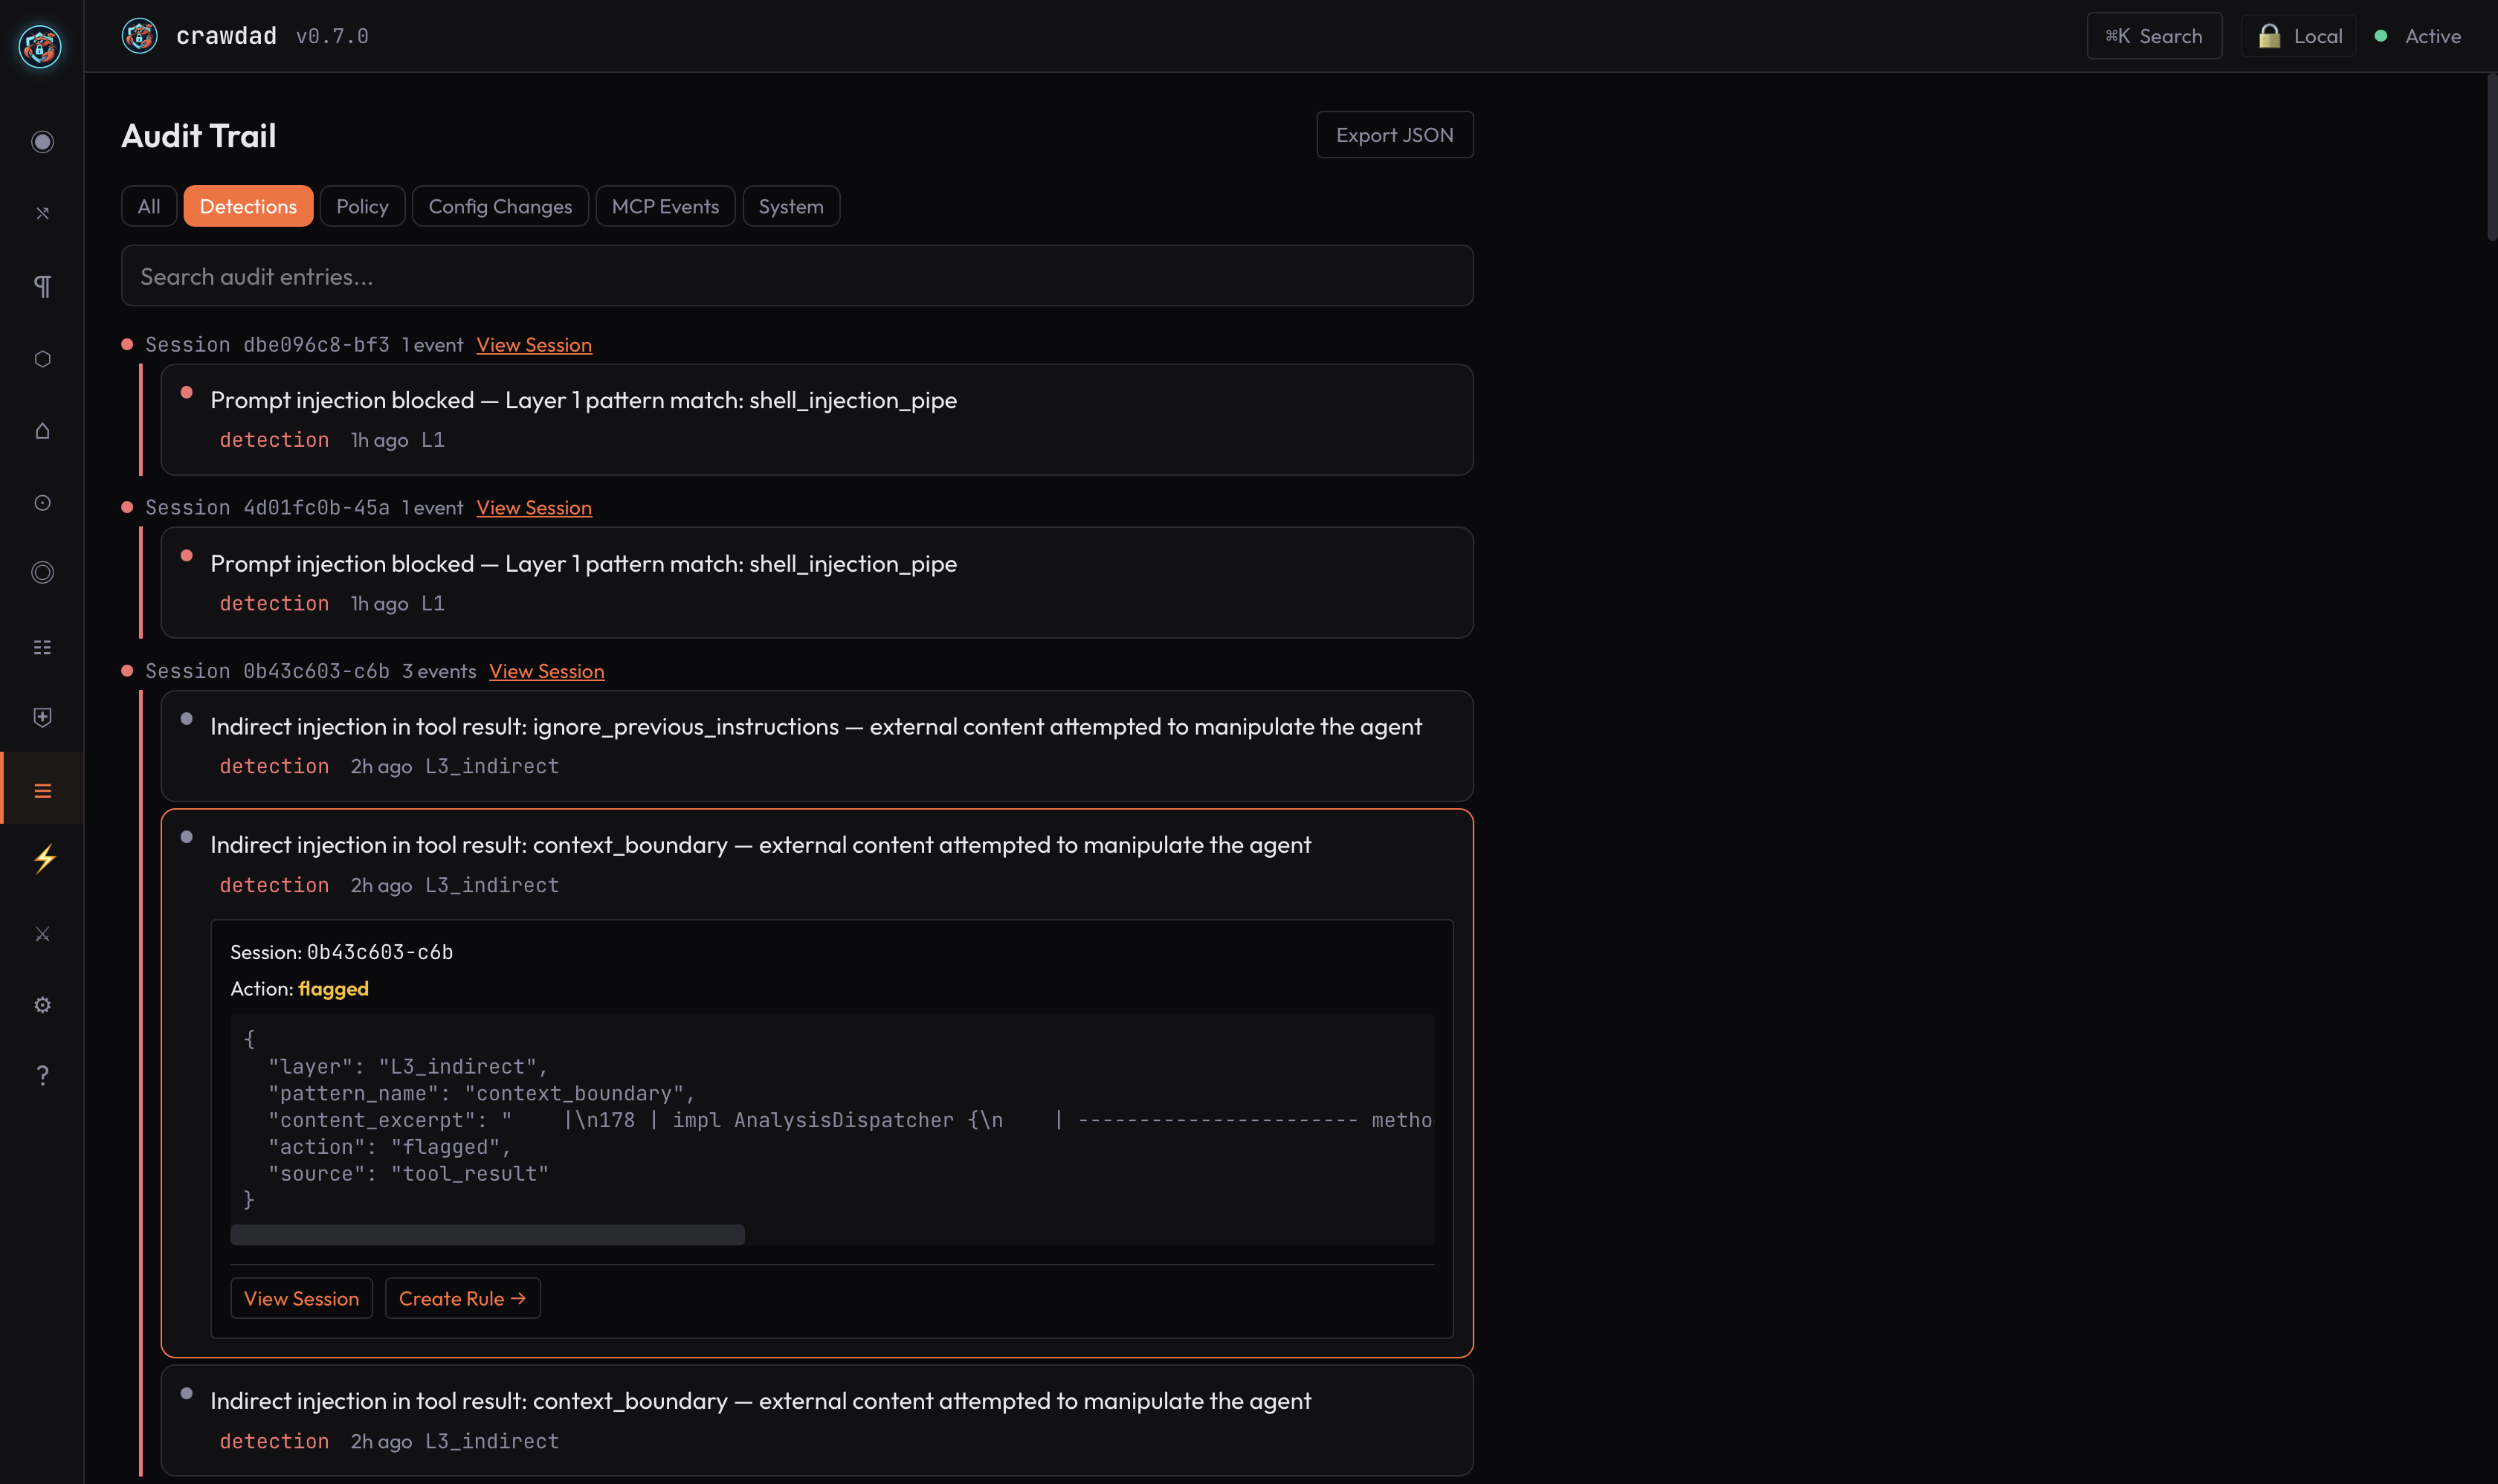
Crawdad Audit Log, tamper-evident, hash-chained event trail

Audit log, tamper-evident, hash-chained event trail for every inspected request

Governed by purpose. Enforced on the action, not the claim.

For a review board, the governance question is not what an agent was told to do, but what it actually did, and whether that fits its authorized purpose. Crawdad governs each agent by an operator-declared charter it cannot see or edit, judges the observed action rather than the stated intent, and watches the whole session for staged compromise. Every decision is made on-device and written to the tamper-evident, hash-chained audit trail your team can verify independently.

Charters: govern by purpose

An operator writes a charter, held outside the agent's control, declaring the agent's real job as an allowlist over three axes: the tools it may call, the data (paths, hosts, recipients) it may touch, and the effects it may produce. Crawdad checks the observed action, so a deceptive stated intent buys nothing, and an out-of-charter action is blocked at the wire with the axis named. The identical request from two agents can get two verdicts, because the charter decides, not the bytes.

Capability Target Effect

Trajectory: watch the whole session

A sequence of individually-allowed steps, enumerate then read progressively more sensitive in-scope data then send, can still compose toward harm. Crawdad measures that shape with deterministic signals anchored to resource sensitivity, and gates an on-device reasoner onto the genuinely ambiguous cases. With no local model reachable, a completed staging chain is held for review, never silently allowed. The false-positive cost on ordinary multi-step work is measured at zero. It does not claim to catch every composed harm; it catches staged compromise that carries a sensitivity climb.

Escalation-shape 0 benign FP

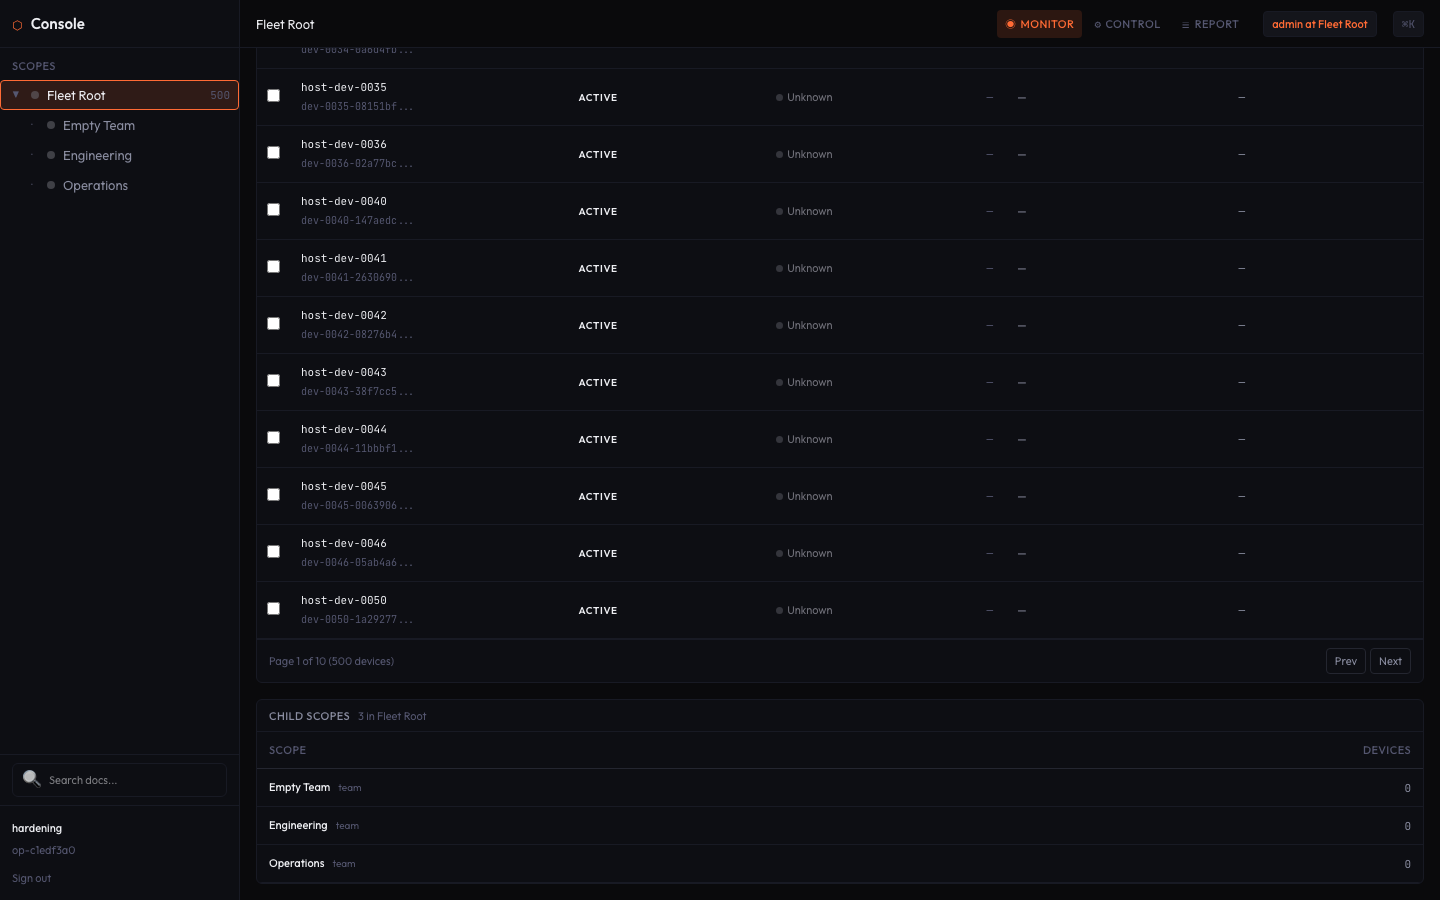
Every decision is legible and reviewable. An operator sees the live governance feed and per-session risk from the local dashboard, authors a charter that governs at the wire on the next action, and approves or denies a held action with a real effect on the running engine. Across sites, the self-hosted console rolls governance up per deployment, distributes charter templates that devices load, and surfaces held actions for triage, over the same signed channel every other fleet command uses. Content never leaves the device: only the resource identifier, the axis, the signals, and the verdict travel.

Security controls that match regulatory expectations.

Crawdad runs as a local proxy on each device. Raw content, prompts, responses, documents, never leaves the machine by default. Metadata-only telemetry (counts, categories, verdicts) egresses by default; raw content never does. Telemetry depth is customer-governed. The architecture is designed to satisfy the data-residency and access-control requirements that regulated industries demand, without requiring you to trust a third-party cloud with sensitive content.

  • Architected for SOC 2 controls, mapped to the Trust Services Criteria
  • Built in Rust, 3,737 automated tests across 26 crates, mechanically counted 2026-08-22
  • Multi-layer detection pipeline

Local-first

Raw content never leaves the device by default. Inspection, detection, and enforcement all happen on-machine. Metadata-only telemetry egresses by default; content does not.

Metadata-only telemetry

Metadata-only telemetry by default. The fleet console sees detection counts and posture signals, never raw prompts or responses.

Runs fully offline

Fully functional with no outbound connectivity. Detection, enforcement, and audit logging operate entirely offline.

Tamper-evident audit log

Hash-chained event trail. Each entry is cryptographically linked to its predecessor, tampering breaks the chain and is detectable.

Signed floors

Policy floors are cryptographically signed. Local users cannot silently lower enforcement thresholds set by the organization.

Visibility across every site. Content stays local.

The Fleet Console gives security teams centralized visibility across every deployment, detection trends, posture signals, policy status, while raw content remains on each device. Multi-site, multi-region, or fully offline: the same architecture scales.

  • Fleet Console, centralized posture across all sites
  • Per-site and per-device policy enforcement
  • Hash-chained audit log on every device
  • Metadata-only telemetry by default
  • Air-gap mode for isolated environments
Fleet Console, centralized visibility across every regulated deployment

Fleet Console, centralized management, metadata-only telemetry

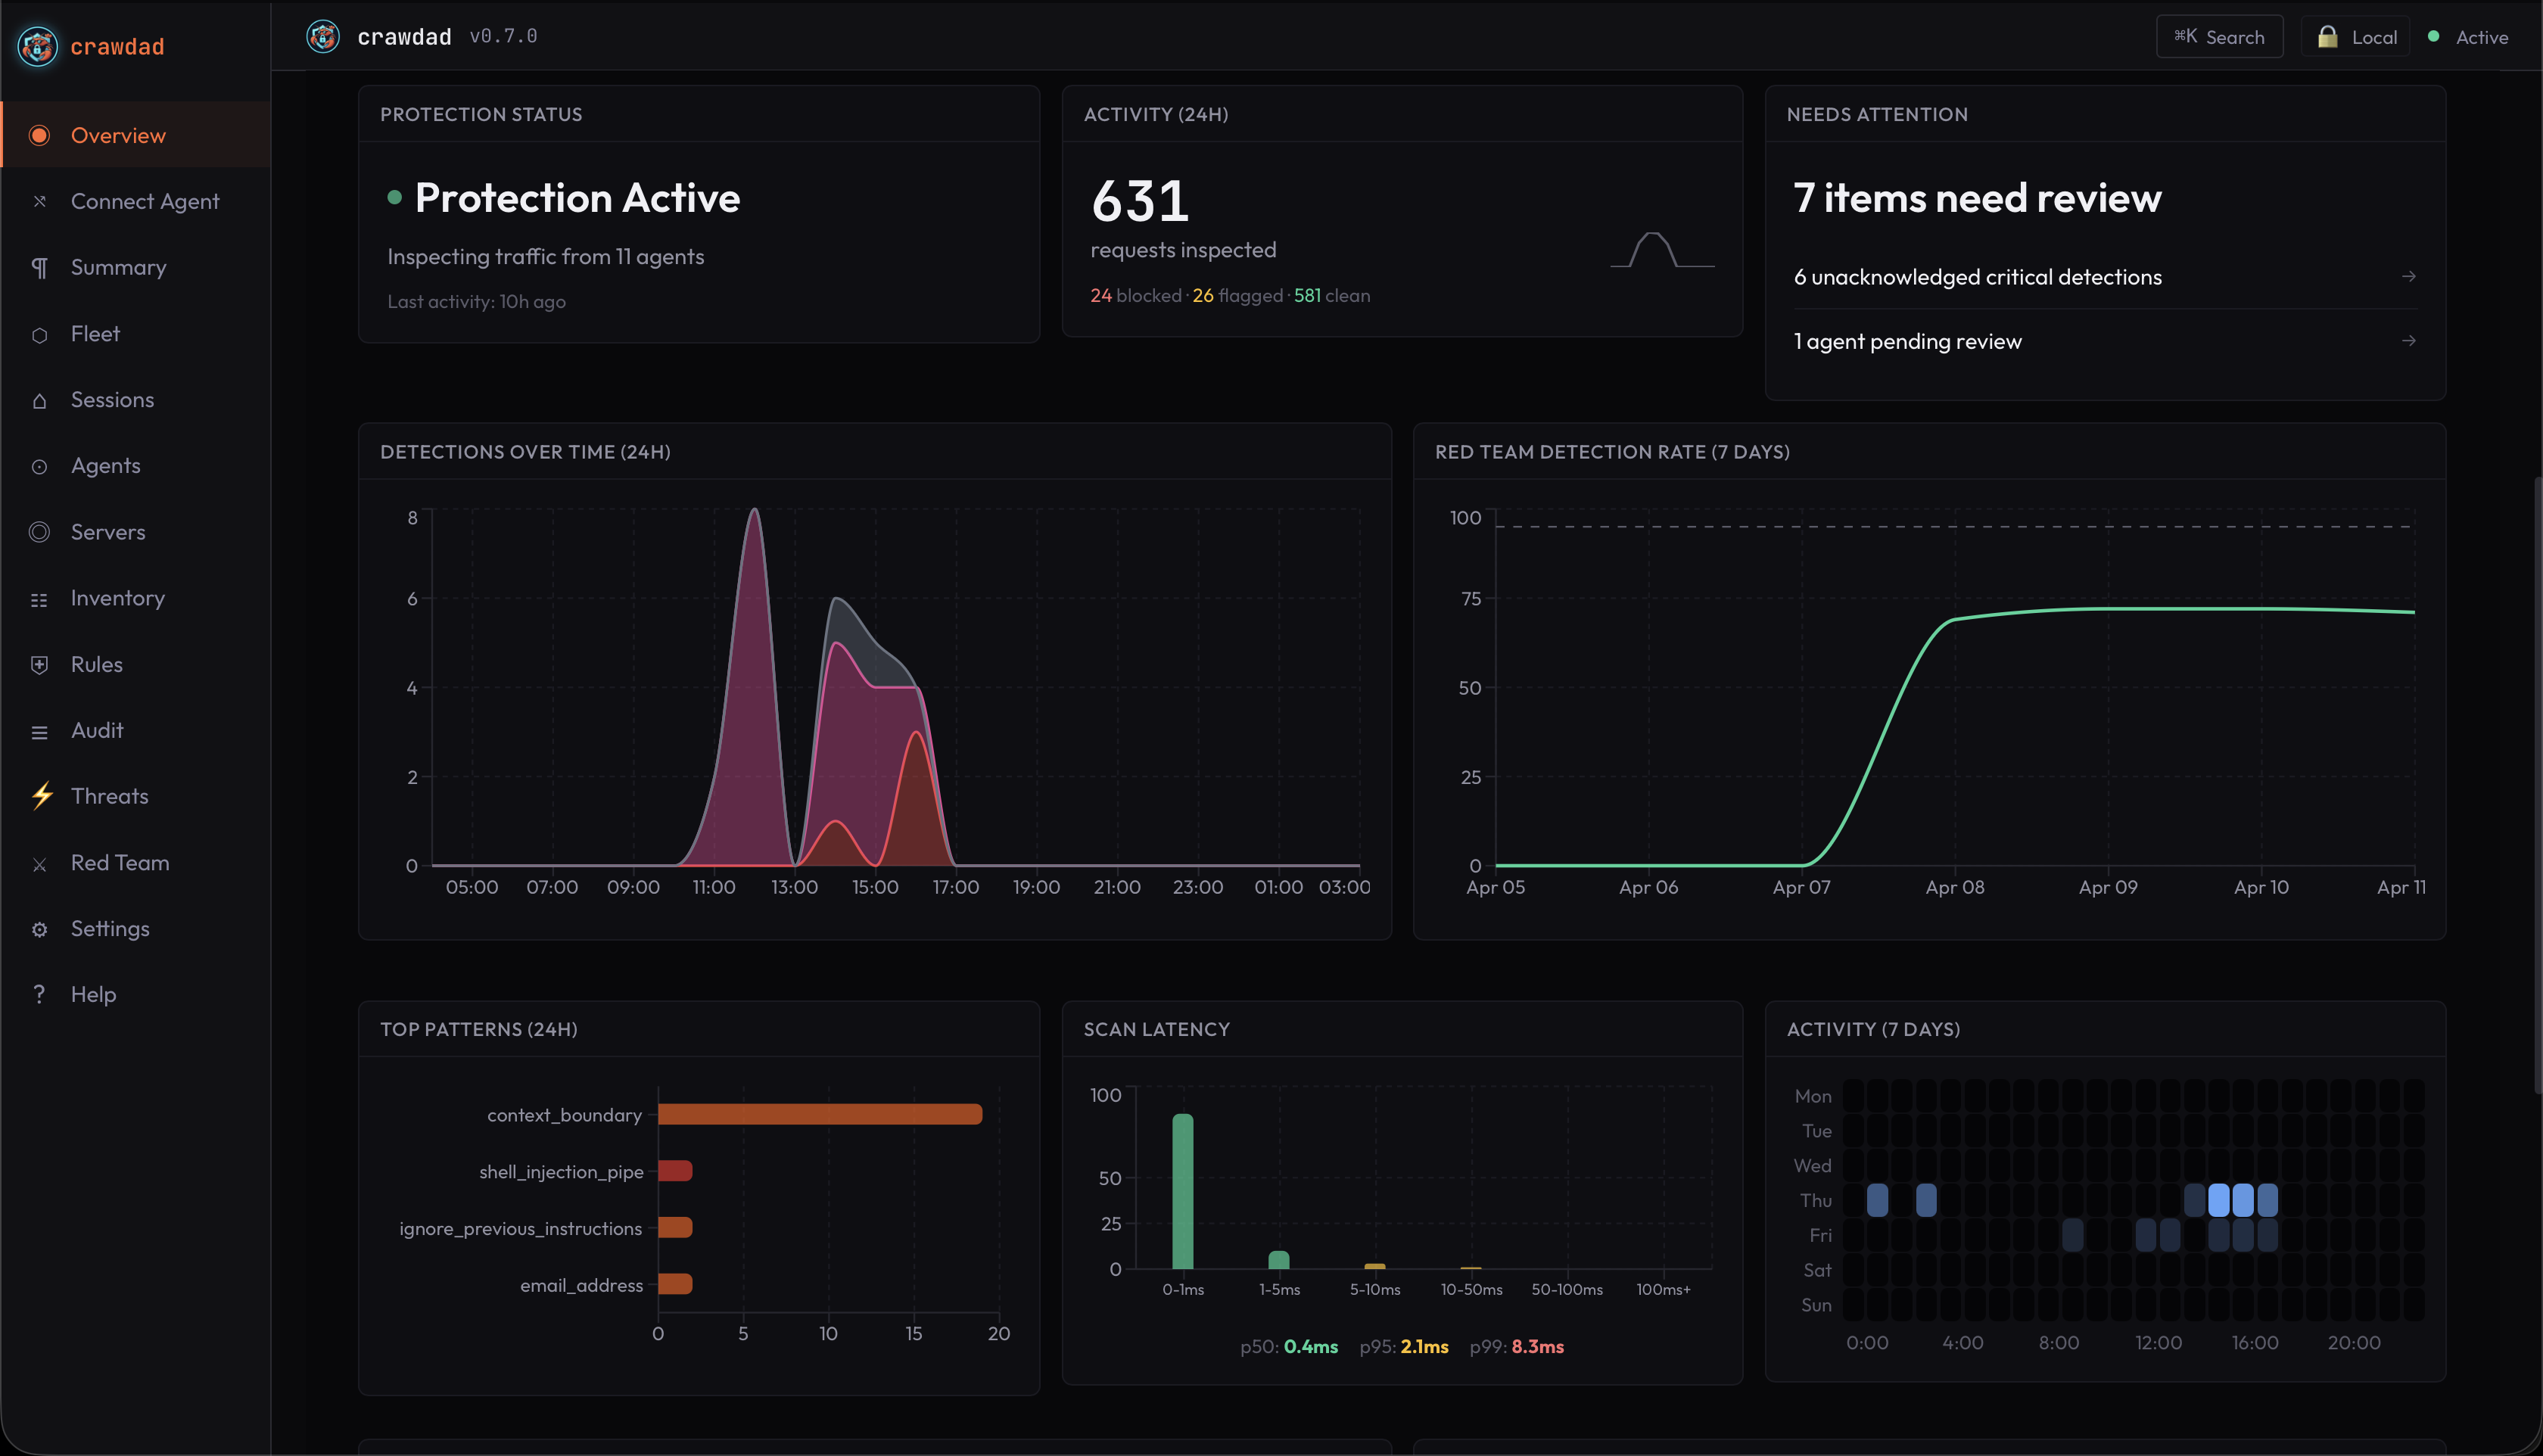
Crawdad Dashboard, real-time detection trends, agent activity

Per-site dashboard, detection trends and agent activity

Architected for the verticals where the rules are strictest.

Every deployment keeps raw content on-device. The controls map to the frameworks your industry answers to, and none of it asks you to trust a third-party cloud with sensitive content.

🏥

Healthcare

PHI never leaves the device. Inspection and enforcement happen on the machine, and metadata-only telemetry (counts, verdicts) is all that egresses, so protected health information is never in it. The controls map to HIPAA and HITECH obligations for the agents handling that data.

HIPAA HITECH
🏦

Financial Services

Architected for environments governed by GLBA, SEC recordkeeping, and financial data protection requirements. The on-device model means sensitive financial data stays on the institution's own infrastructure. Tamper-evident audit logs support recordkeeping and examination readiness.

GLBA SEC 17a-4 SOX
🏛

Government

Federal, state, county, and local agencies face strict data-sovereignty requirements. Crawdad runs fully offline and on-premises, so data stays within sovereign boundaries with no external cloud dependency.

Data sovereignty Offline On-prem

Utilities & Critical Infrastructure

Operational technology environments cannot tolerate external data flows. Crawdad runs fully offline with no outbound connectivity, which aligns with NERC CIP and critical-infrastructure protection obligations.

NERC CIP ICS/SCADA
🛡

Insurance

Insurance organizations handle sensitive policyholder data across underwriting, claims, and actuarial workflows. Content stays local and audit trails are tamper-evident, mapping to state insurance data-security regulations and the NAIC model law.

NAIC Model Law State regs
497 real attacks on a public, reproducible benchmark

The detection engine is measured on this public corpus; on the proxy path the arbiter blocks what it detects. Detection and blocking are named as separate mechanisms, on purpose, and the corpus is open so you can run it yourself. How detection becomes blocking →

497attacks tested
1,669total samples
22attack categories
1missed attack
Every result is published, including the misses. We’re not aware of another vendor in the category that ships a reproducible, clone-and-run benchmark at all. Clone the corpus, run it against us or anyone, and compare. Every number here is reproducible.

Multi-layer detection pipeline. Built in Rust. 3,737 automated tests across 26 crates, mechanically counted 2026-08-22. Raw content stays on the device by default, metadata-only telemetry by default (none at all when run fully offline).

AndrewSispoidis/contemporary-agent-attacks →

CC BY 4.0 · 497 attacks · 1,172 benign negatives · 22 categories

For your review board, stated plainly: full runtime enforcement runs on macOS and Linux. SOC 2 is architected-for, not certified, and we publish the control mapping so your team can evaluate the fit. A macOS System Extension for system-wide interception is built and pending an Apple entitlement; until it is granted, protection covers agents routed through Crawdad rather than every process on the machine. See the full trust posture →

AI agents are already inside your environment. Secure them without moving data.

Talk to us about deploying Crawdad in your regulated environment. We’ll walk through the architecture, the deployment model, and how the controls map to your compliance requirements.

Talk to Us → Architecture Docs

Get in Touch

Tell us about your needs and we'll follow up.